Time records are personal data
The General Data Protection Regulation (GDPR) has applied across the EU and EEA since 25 May 2018. In the UK, the same rules continue as the UK GDPR alongside the Data Protection Act 2018, as amended by the Data (Use and Access) Act 2025. Under Article 4 GDPR, personal data is any information relating to an identified or identifiable person. That includes everything a time tracking system records about an employee:
- clock-in and clock-out times, breaks and total hours;
- the site or client where the employee worked;
- the position recorded at clock-in, if you use GPS;
- absences, holiday and overtime.
As the employer, you are the controller: you decide why and how the data is processed and you are accountable for it. A time tracking provider that processes the data on your behalf is a processor. One detail is often missed: the reason for a sickness absence is health data, which GDPR treats as a special category. Record "sick leave", not the diagnosis, unless a specific rule requires more.
Choosing a lawful basis
Every processing purpose needs one of the lawful bases in Article 6. For attendance data, three are realistic and one is usually a trap:
| Lawful basis | When it fits | Watch out for |
|---|---|---|
| Legal obligation, Art. 6(1)(c) | National law requires you to record working time, as in Spain, Germany, Romania or the UK working time records | Covers what the law requires; it does not automatically cover extra data such as location |
| Contract, Art. 6(1)(b) | Calculating pay, overtime and holiday under the employment contract | The processing must be genuinely necessary for the contract |
| Legitimate interests, Art. 6(1)(f) | Checking that a clock-in happened at the work site, preventing one worker clocking in for another, planning | Needs a documented balancing test, and employees have a right to object |
| Consent, Art. 6(1)(a) | Rarely appropriate at work | Because of the imbalance of power, consent from employees is seldom freely given |
In practice, many employers rely on legal obligation or contract for the hours themselves and on legitimate interests for the location check at clock-in. Write the reasoning down. A short legitimate interests assessment answers three questions: what is the purpose, is the processing necessary for it, and do the employees' interests override yours?
The GDPR principles applied to attendance data
Article 5 sets out the principles every processing operation must respect. For time tracking, they translate into concrete decisions:
- Lawfulness, fairness and transparency: a lawful basis for each purpose, and employees told in advance.
- Purpose limitation: data collected to record attendance should not quietly become a tool for unrelated performance monitoring.
- Data minimisation: collect what the purpose needs. A position at clock-in and clock-out, not a movement history.
- Accuracy: let employees see their own records and correct mistakes quickly.
- Storage limitation: keep records for the period national law requires, then delete or anonymise them.
- Integrity and confidentiality: restrict access by role and secure the system.
On top of these sits accountability: you must be able to show how you comply, with a record of processing activities, your assessments and your privacy notice.
Is GPS time tracking legal under GDPR?
GDPR does not ban GPS at work. It asks whether the processing is necessary and proportionate for a legitimate purpose, and whether a less intrusive method would do the job. For attendance, the line usually falls like this.
Usually proportionate
- Recording the position only at the moment of clock-in and clock-out.
- Using it only to confirm that the employee was at the work site, checked against a geofence for that site.
- Telling employees in writing before the system goes live.
- Limiting access to the managers who need it and keeping the data no longer than necessary.
Usually disproportionate or high risk
- Continuous tracking during the whole shift without a specific, documented need.
- Any tracking outside working hours or during breaks.
- Covert tracking, or location used to score performance rather than to verify attendance.
Always ask the necessity question. For a fixed site such as a shop or office, a QR code at the entrance may prove presence with no location data at all. For teams that move between building sites or client premises, a single position at clock-in is often the least intrusive reliable option. Some authorities take a strict line: France's CNIL, for example, considers that geolocation should not be used to control working time where another means is available.
With a browser-based app, the phone's own permission prompt controls access to location. NoBadge captures position only at clock-in and clock-out and does not track employees in between.
NoBadge records location at 2 moments per shift, clock-in and clock-out, and checks it against the geofence of that site. There is no tracking during the shift.
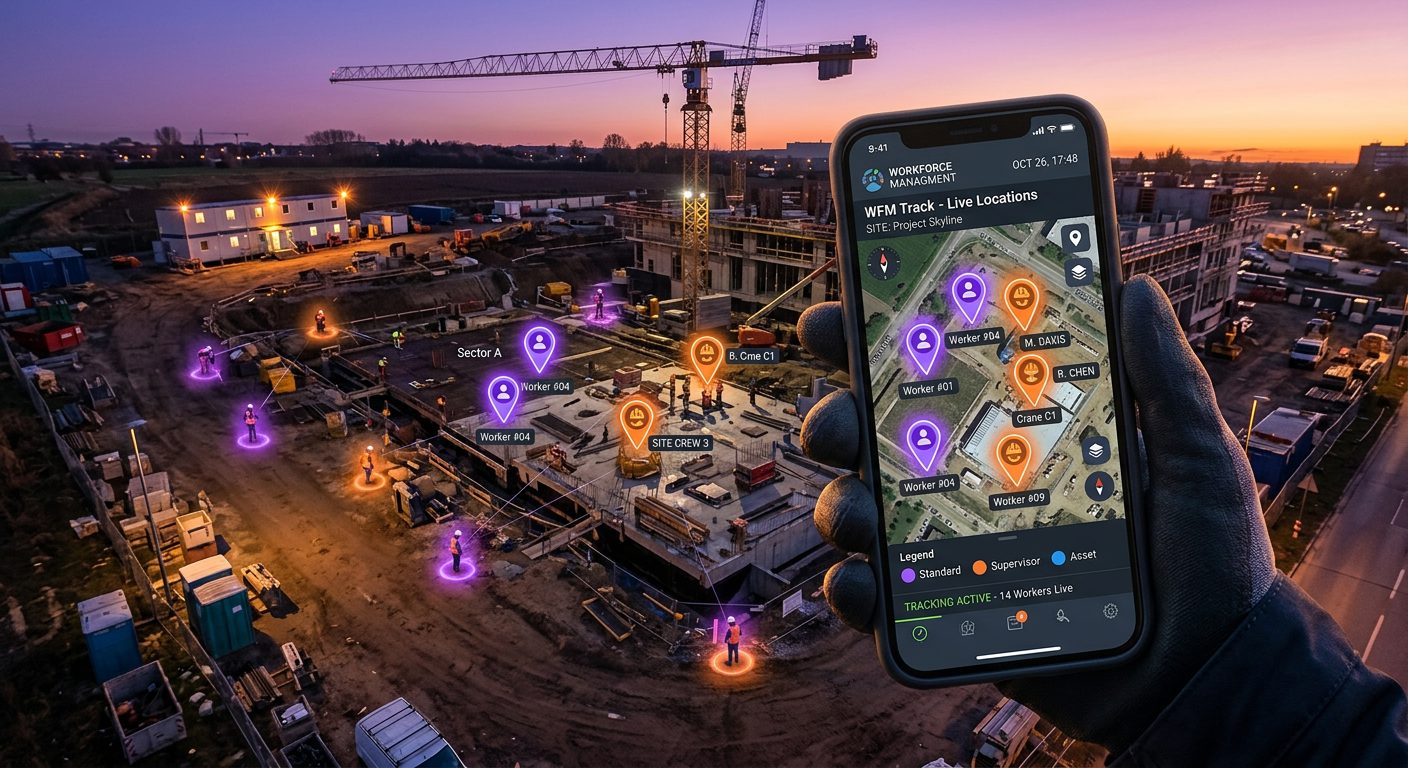
GPS clock-in designed to be proportionate
Position captured only at clock-in and clock-out, a geofence per site, role-based access and data on EU servers. See how the NoBadge GPS time clock works.
QR codes, badges and biometrics
Fingerprint and face-recognition clocks process biometric data to identify people, which is special category data under Article 9 GDPR. It needs a specific condition on top of a lawful basis, and employee consent is rarely a solid one. Regulators have taken a restrictive line: Italy's Garante and France's CNIL have repeatedly questioned biometric clock-ins, and in 2024 the UK ICO ordered a leisure operator to stop using facial recognition and fingerprint scanning to monitor staff attendance.
A QR code time clock avoids the problem. The employee scans a code at the entrance with their own phone, and the system records who scanned it and when, with no biometric data. With NoBadge the code changes every few seconds, so a photo of it shared in a group chat is useless a moment later. Traditional badges also avoid biometrics, but a badge can be lent to a colleague.
The privacy notice: what to tell employees
Articles 13 and 14 require you to inform employees before processing starts. For a time tracking system, the notice should cover at least:
- who the controller is, with contact details, and the data protection officer if you have one;
- the purposes (recording working time, pay, verifying presence at the site) and the lawful basis for each, including the legitimate interest where you rely on it;
- which data is collected: timestamps, site, and position at clock-in and clock-out if you use GPS;
- who receives it: your software provider as processor, your payroll provider or accountant;
- any transfer outside the EEA or UK and the safeguards used;
- how long each type of record is kept;
- the employee's rights: access, rectification, erasure where applicable, restriction, objection and portability, and the right to complain to the supervisory authority.
Write it in plain language, give it before the first clock-in and keep a dated copy. Where employee representatives have a say, consult them first: in Germany, for example, the works council has co-determination rights over systems that can monitor employees.
When you need a DPIA
A Data Protection Impact Assessment is required under Article 35 when processing is likely to result in a high risk to people's rights. European guidance lists criteria such as systematic monitoring, data concerning vulnerable people (employees are treated as such because of the imbalance of power) and the use of new technology. As a rule of thumb, processing that meets two criteria usually needs a DPIA.
For GPS time tracking, assume a DPIA is expected or at least wise. The UK ICO's list of high-risk processing includes tracking geolocation in an employment context, and other authorities publish similar lists. For a QR code clock-in without location, the case is weaker, but documenting a short assessment is still good practice.
- A description of the processing: what is collected, when, from whom, by which tool
- Why it is necessary and proportionate, and which less intrusive options you considered
- The risks to employees, such as misuse of location data or unauthorised access
- The measures that address them: clock-in-only location, geofences, access roles, retention limits
Your software provider: DPA, hosting and security
Under Article 28, you need a written data processing agreement (DPA) with any provider that processes employee data for you. It sets out what the processor may do with the data, its security measures, the use of sub-processors and what happens at the end of the contract. NoBadge provides a DPA on request; details are in our privacy policy.
Check where the data is hosted. Transfers outside the EEA are possible only with an adequacy decision or appropriate safeguards such as standard contractual clauses. NoBadge stores data on EU servers. Then look at security under Article 32: who can see what, how accounts are removed when someone leaves, and how access is controlled.
- Where is the data hosted, and which sub-processors are used?
- Is a DPA available, and what does it say about deletion at the end of the contract?
- Are there separate roles, so employees see only their own records and managers only their teams?
- Can you export records to answer an access request or a labour inspection?
NoBadge uses three roles, admin, manager and employee, so each person sees only what they need, and exports complete records to Excel in one click.
National rules on top of GDPR
GDPR sets the baseline; employment law in each country decides whether and how working time must be recorded. In its 2019 judgment in case C-55/18, the Court of Justice of the EU held that member states must require employers to set up an objective, reliable and accessible system for recording each worker's daily working time. Countries have implemented this differently:
Germany
The Federal Labour Court ruled in 2022 that employers are already obliged to record working time under occupational health and safety law. The Working Time Act requires hours beyond eight a day to be recorded and kept for two years. A law setting out the details has been announced; check its current status. Works councils have co-determination rights over time tracking systems.
Spain
Since May 2019, every employer must keep a daily record of each employee's start and finish times, keep it for four years and make it available to employees, their representatives and the Labour Inspectorate. Failure to do so can lead to fines. Reforms towards a mandatory digital register have been discussed; check the current position.
France
Employers must be able to count the hours of staff who do not all follow the same collective schedule. Employees must be informed individually before a monitoring tool is introduced, and the social and economic committee (CSE) must be informed and consulted. The CNIL is strict about geolocation used to control working time.
Romania
The Labour Code requires employers to keep a record of the hours worked each day by each employee, showing start and finish times, and to make it available to the Labour Inspectorate. Law 190/2018, which implements GDPR, adds conditions for electronic monitoring of employees, such as prior information and consultation of the union or employee representatives; check whether they apply to your setup.
United Kingdom
The UK GDPR and the Data Protection Act 2018 apply, enforced by the ICO, whose 2023 guidance on monitoring workers stresses transparency, proportionality and DPIAs. The Working Time Regulations 1998 separately require records adequate to show compliance with the 48-hour limit, kept for two years. Our Working Time Regulations UK guide covers those rules in detail.
An eight-step checklist for SMEs
- Map the data: list what you record, why, and who sees it.
- Pick a lawful basis for each purpose, and write a legitimate interests assessment for the location check.
- Choose the least intrusive method per site: QR code for fixed sites, GPS at clock-in for field teams.
- Carry out a DPIA if you use location data or other monitoring.
- Inform employees with a privacy notice, and consult representatives where required.
- Sign a DPA with your provider and check hosting and sub-processors.
- Set access roles and a retention schedule based on the national record-keeping period.
- Review once a year and handle access requests, normally within one month.
This article is general information, not legal advice. For guidance specific to your organisation and country, consult a data protection adviser or employment lawyer.